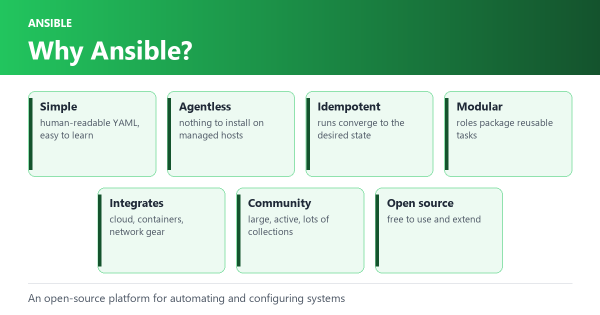
Ansible is an open-source software platform for automating and configuring computer systems.
In this blog I will use kubectl to create a ClusterRole and a ClusterRoleBinding (refer to link)
{ "kind": "ClusterRole", "apiVersion": "rbac.authorization.k8s.io/v1", "metadata": { "name": "myclusterrole", "creationTimestamp": null }, "rules": [ { "verbs": [ "get", "list", "watch" ], "apiGroups": [ "" ], "resources": [ "persistentvolumes" ] } ] } k create clusterrole myclusterrole --verb=get,list,watch --resource=persistentvolumes k describe clusterrole myclusterrole You can use a ClusterRole to
define permissions on namespaced resources and be granted within individual namespace(s)
define permissions on namespaced resources and be granted across all namespaces
define permissions on cluster-scoped resources
The CPU operates in two modes in Linux
User mode (non privileged mode) Kernel mode (System mode) When operating in Kernel mode it has un-restricted access to resources like memory and input output devices.