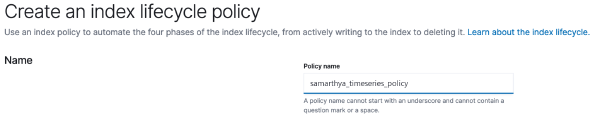
Timeseries is a data stream that is defined for a set of fields over a time period. Some examples may include, daily attendance register for an organization, wherein people punching in every-morning will be different, missing mostly for weekends or on planned and unplanned leaves.
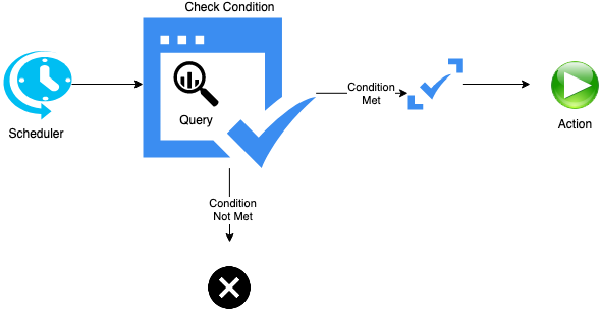
Watcher # Watcher is an Elasticsearch feature that facilitates alerting and can be used to create actions based on conditions, which are periodically evaluated using queries on your data. There are two ways of creating a watcher
Aggregation works on a group of documents and can be categorized
Metric Pipeline Bucket Matrix Metric Aggregation # Computes a single or multiple values
It is a short howto guide which shall talk about adding a LDAP realm to an Elasticsearch 7.6.2 cluster.
Realms # It is a concept not alien to IDAM professionals. In simple words it is a system that allows you to authenticate and authorize an incoming request. It will define the entity USER, that may include at a bare minimum (not limited to)
Text is a key data in most of the information that is ingested in the elasticsearch, and whether it is type text or keyword it requires careful consideration to choose which analyzer to use.
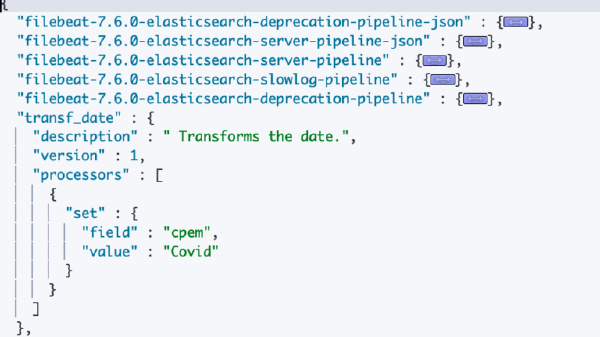
Pipelines is a smooth way of processing some incoming data. In this blog, I will walk through some of the items I have tried my hands on.
Pipeline # A pipeline is a definition of a series of processors that are to be executed in the same order as they are declared.
I will extrapolating based on the original documentation available here and based on some of my experience using this API.
It copies documents from one index to another.
Extracts the document source from the source index and indexes the documents into the destination index. You can copy all documents to the destination index, or reindex a subset of the documents.
Open specification for document fields for data ingested in Elasticsearch. It brings uniformity to certain common fields that are used across data sources.
ECS defines two field levels
Core fields: Represent the fields that are most common across all use cases. Extended fields: That are not part of the core and specific to cases. Field sets # Field sets are multiple groups of related fields defined by ECS. More information here.
If you are not aware of mapping, it might be a little confusing but I would try my best.
Every document that gets indexed in elastic has fields, every field that is accessible has an associated type with it (Inverted Index) which helps elastic organize data for quick retrieval.
In this post I will try to enable security for the elasticsearch cluster. It would be simply penned as a sequence of steps you need to follow to enable security as part of the cluster.
In the previous blog we searched for a match\all, and sorted it by age. In this we will improve upon the query we are writing and look for other options.
What I have been doing is evaluating Elasticsearch. The indexing, searching (Phrase, Similarity, Structured, Full Text, Complex), clustering etc. In this blog I will just try and simplify the learning curve.