↓ Skip to main content
Security

Security Analytics

Table of Contents
* Header image from Elastic.co

As we move towards the micro-service/container economy where there are heaps of products available in form of applications to be downloaded & installed on primarily two platforms Android and IOS, we just cant underline the security implications enough.

SIEM - Security information and Events management.

In this blog, I will walk through the enabling-platform that elastic is. Elastic enables data ingestion from multiple sources, and identifying/predicting threats.
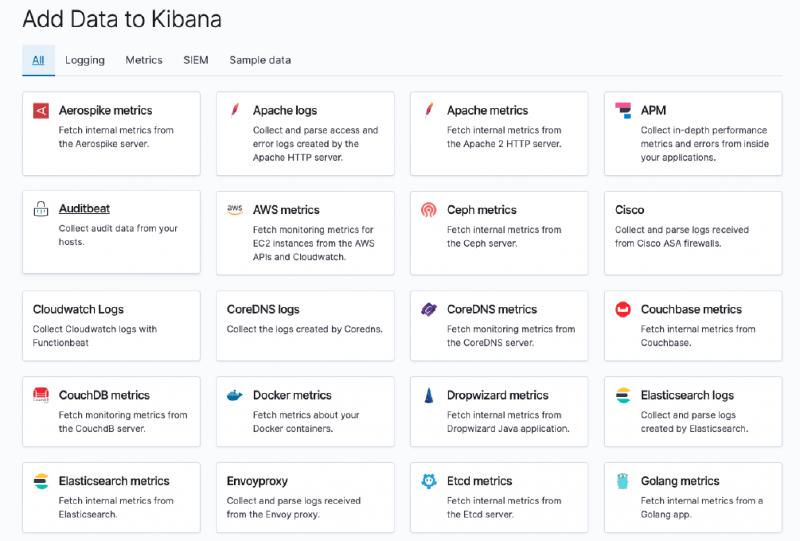
Data sources
Data sources

Data generators
#

The source of truth is always the activity information from an application

ECS
#

Elastic common schema allows to normalize the data from multiple sources. Which allows correlation much easier and eventually more convenient searches for data retrieval and enrichment.

In version 7.2 SIEM was made available.
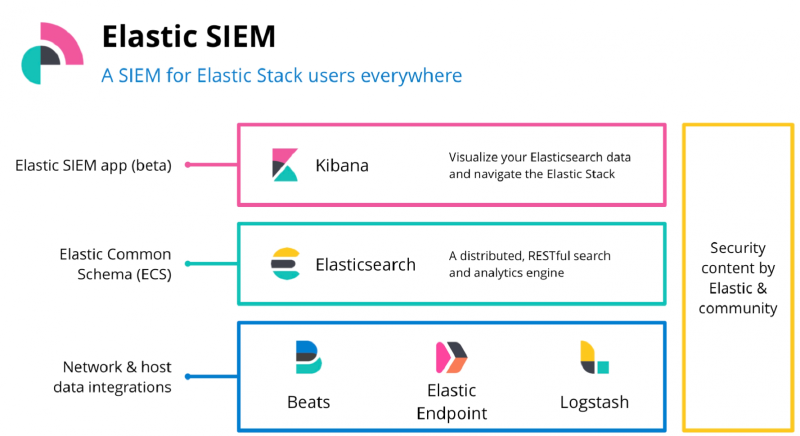
Elastic SIEM architecture: Kibana SIEM app, Elasticsearch with the Elastic Common Schema, and Beats, Elastic Endpoint and Logstash
* Image above is from from Elastic.co
Author
Samarthya
Engineer, learner, tinkerer. This is my trophy shelf of everyday work and leisure.

Related

Spring Data-LDAP

·7 mins
I have a small problem at hand which girdles around learning Angular, with a Spring enabled Rest endpoints which uses a DB to store data and have security layer in between that should interact with a LDAP for authentication and authorization and finally the application should run as one smooth unit. It will be too much to cover in single blog so I will be writing multiple blogs in continuation to this one.

Concurrency

Concurrency and Parallelism – (Helpful link) # Last few weeks have been interesting, a new year just embarked, my learning pace slowed down; comparatively due to the festivities and obligations around, but I am still trying to maintain.