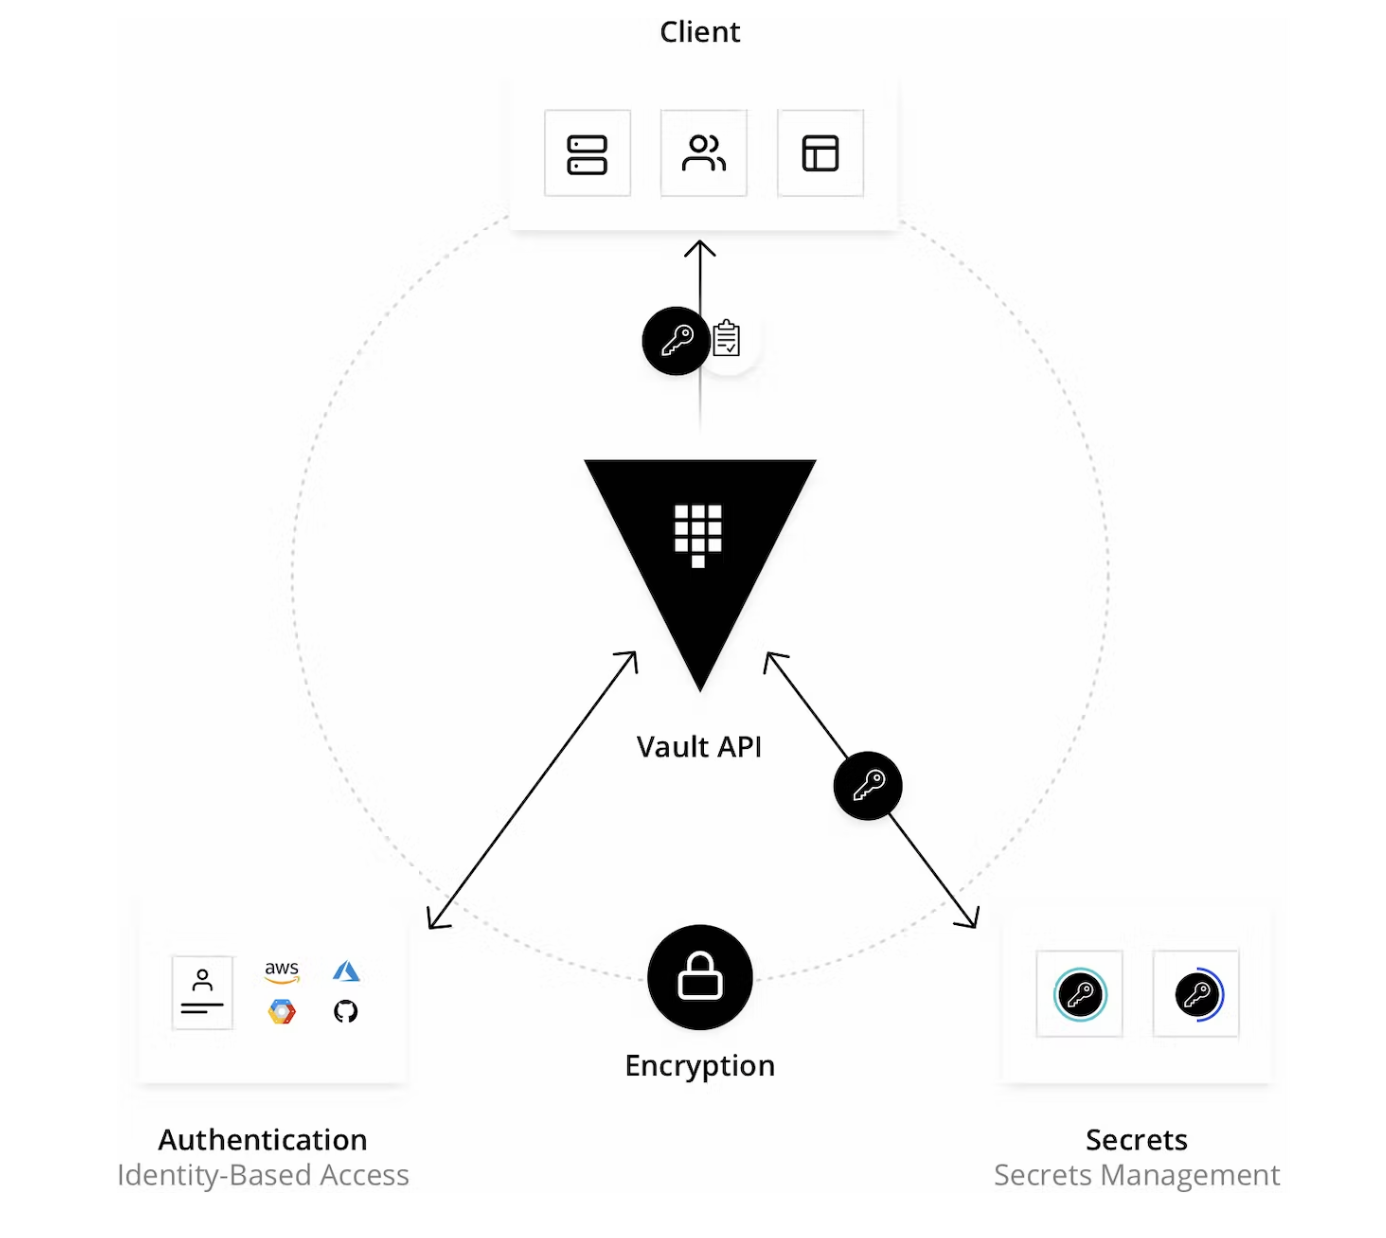
“HashiCorp Vault is an identity-based secrets and encryption management system.”
— Hashicorp
In this blog I am attempting to use the vault for a custom kafka-keystore implementation. Points form the official documentation that you need to remember
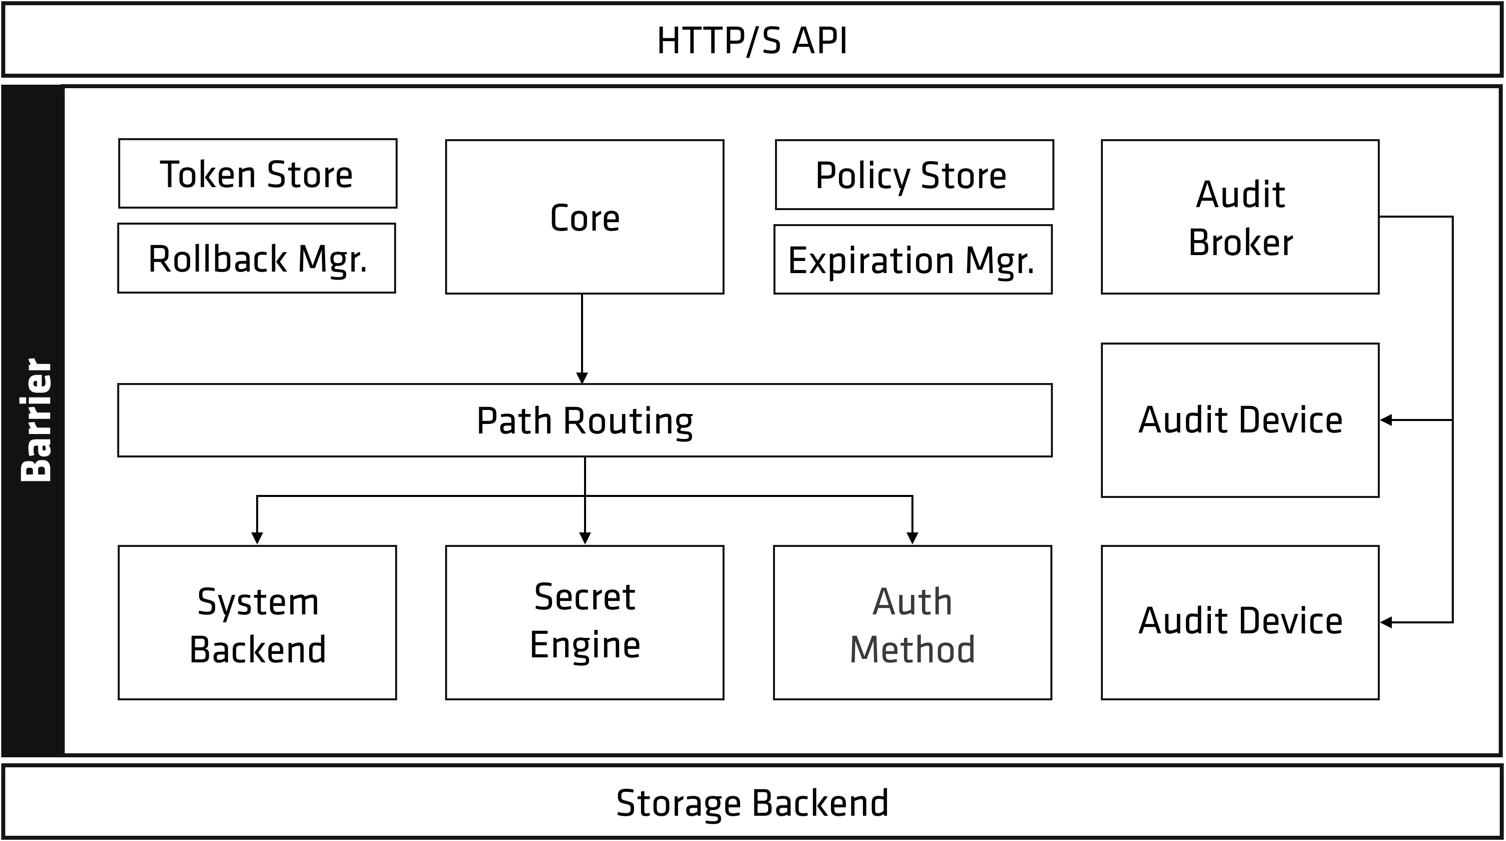
- Vault encryption layer is referred to as
barrierand is responsible for encrypt & decrypt vault data. - Vault writes data to the configured storage in encrypted format.
- Vault starts in
sealedstate & before any operation can be performed it needs to be unsealed. - By default Vault uses Shamir’s secret sharing to split the unseal key (configurable).
- Secret engines are components which store, generate or encrypt data.
- Secret engines are enabled at a path in
Vault. - Once a secret engine is enabled, once can interact with it directly at its path according to its own API.