A scenario in Molecule is a configuration that defines how a role should be tested. It consists of a set of instructions and parameters that determine how a role is provisioned, converged, and verified. The purpose of scenarios is to allow for flexibility in testing a role by allowing multiple testing configurations to be defined and executed. You can have as many scenarios as you like and Molecule will run one after the other.
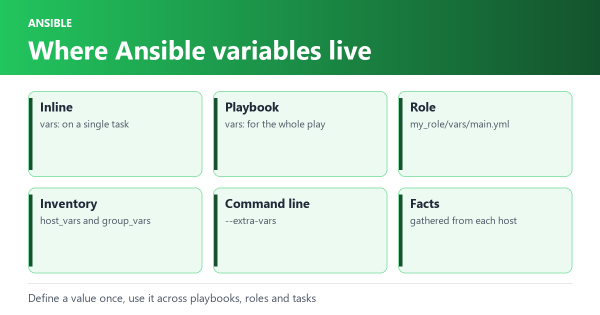
Variables are a crucial part of Ansible and are used to store values that can be used across playbooks, roles, and tasks.
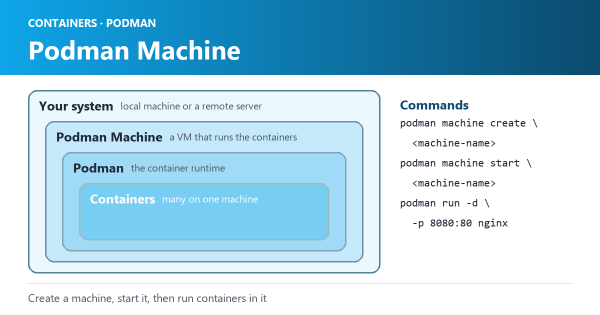
Podman Machine is a tool that allows you to manage multiple Linux containers on your local system or on remote servers.
Buildah is a command-line tool used for building and managing OCI-compliant images. It is an alternative to Docker Build that provides greater flexibility and control over the image building process.
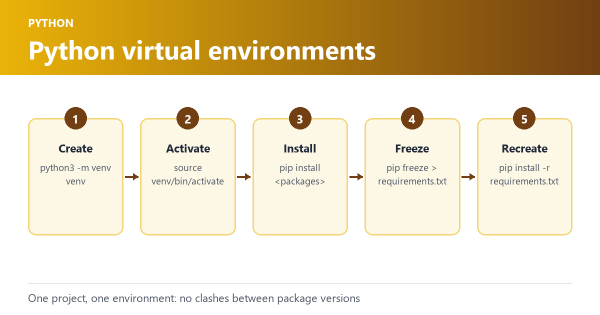
Continuing from the blog, Virtual environments are isolated Python environments that allow you to manage dependencies separately for each project, providing a controlled and reproducible environment…
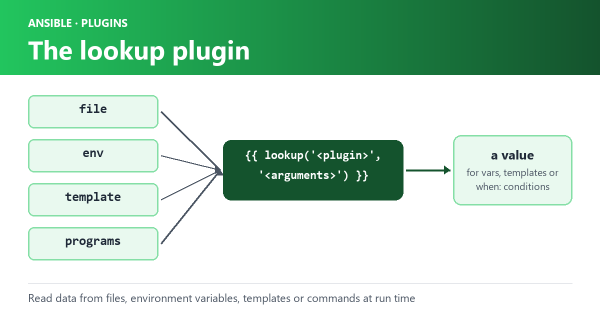
Ansible’s lookup plugin allows you to access data from a variety of sources, including files, templates, and external programs.
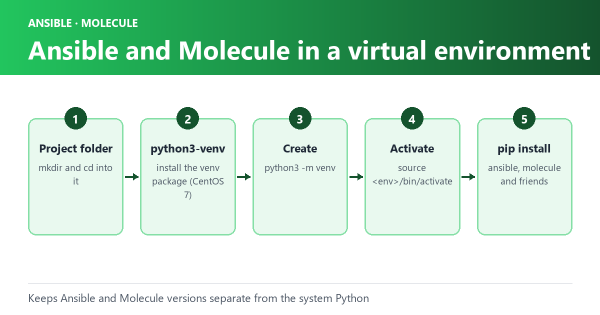
Ansible and Molecule are popular tools for configuration management and testing in the world of DevOps.
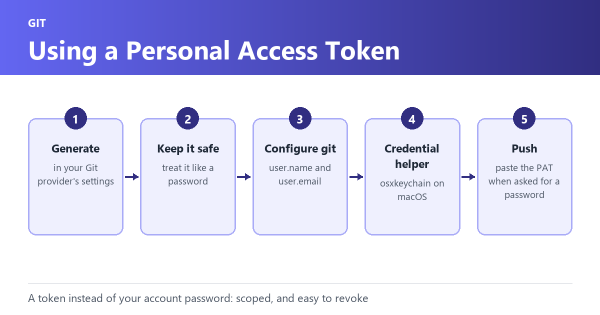
Using Git Personal Access Tokens (PATs) is a secure and convenient way to authenticate with Git service providers.
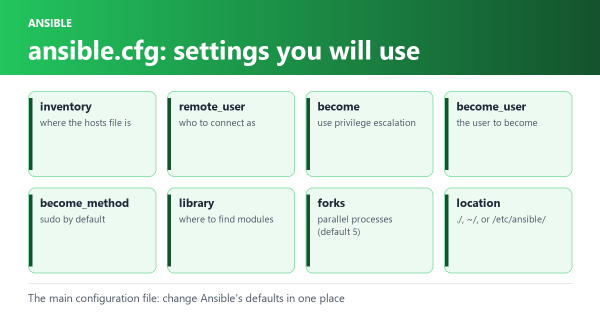
The file can be placed in various locations, such as the current directory, user’s home directory, /etc/ansible/, and /etc/ansible/conf.d/.
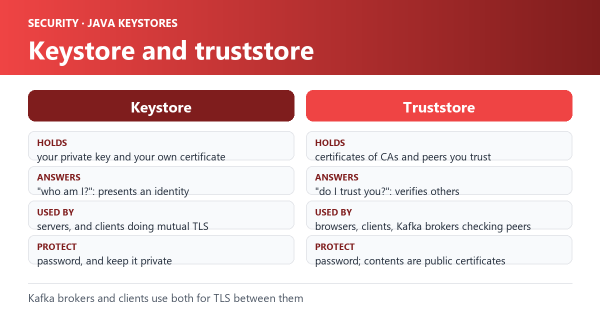
In Apache Kafka, trust store and keystore are essential components for ensuring secure communication between brokers, clients, and other services.
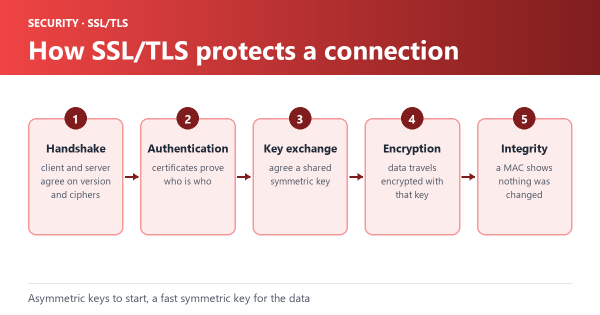
Secure Socket Layer and its successor TLS (Transport Layer Security) are cryptographic protocols that provide encryption, integrity, and authentication for network communication.
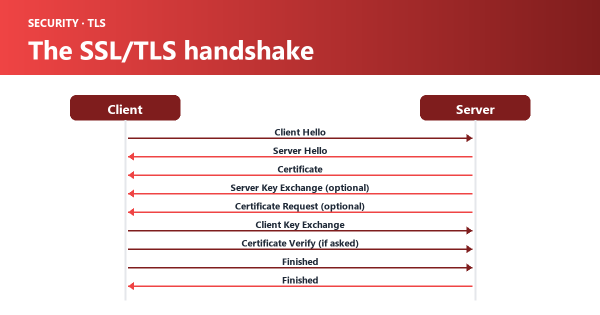
The SSL/TLS handshake is the initial communication between the client and server in a SSL/TLS connection.
Testinfra is a Python-based framework for infrastructure testing. It allows you to write tests for your infrastructure and verify that everything is working as expected.
Ansible Variables are used to store values that can be reused throughout an Ansible playbook.
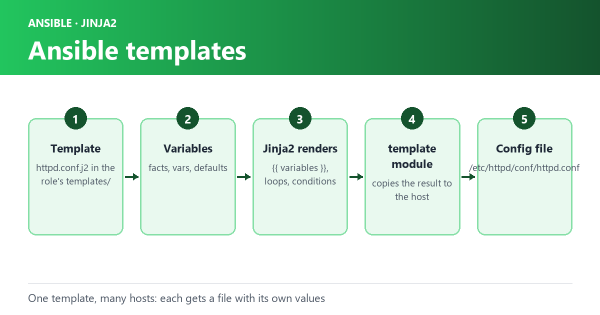
Templates in Ansible are a type of file that contain configuration information or scripts written in a Jinja2 templating language.
To set up SSH access for inventory hosts in Ansible, follow these steps:
An Ansible inventory is a file that defines the hosts and groups of hosts that Ansible will manage. Inventory files are used to define the nodes (hosts) that will be managed by Ansible.
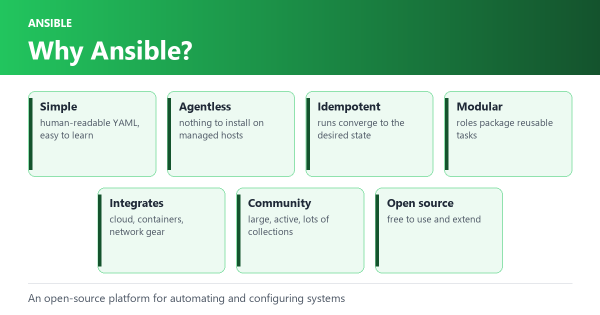
Ansible is an open-source software platform for automating and managing IT infrastructure.
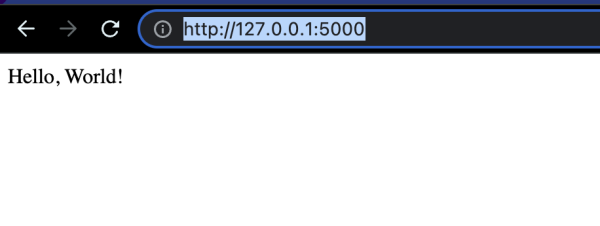
Building a simple hello world using Flask. (The code is available here)
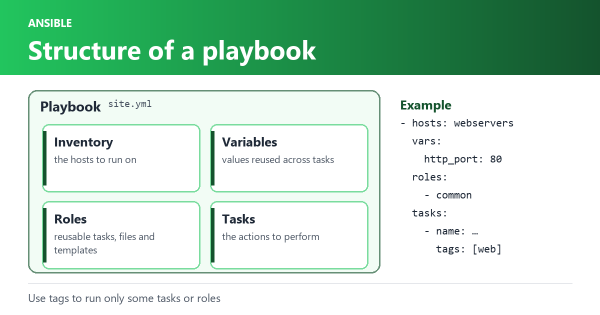
The structure of an Ansible playbook includes the following elements:
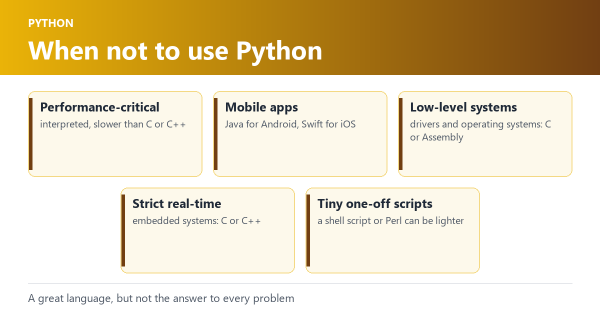
Python is a versatile and widely-used programming language, but there are certain scenarios when it may not be the best choice. Here are some examples of when not to use Python:
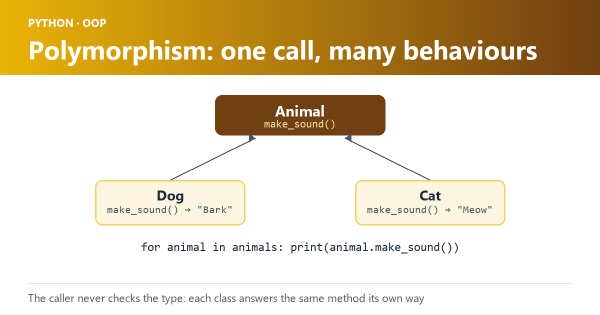
Polymorphism is a key feature of Object Oriented Programming that allows objects of different classes to be treated as objects of a common class.
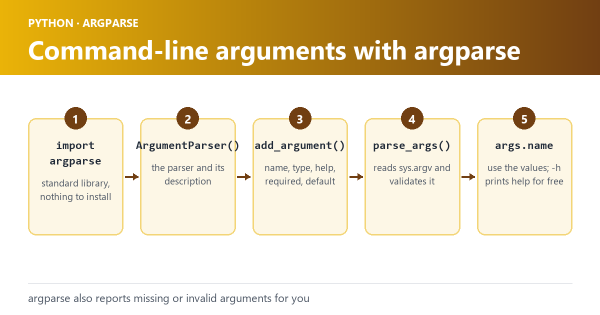
The argparse module is a powerful tool for parsing command line arguments in Python.
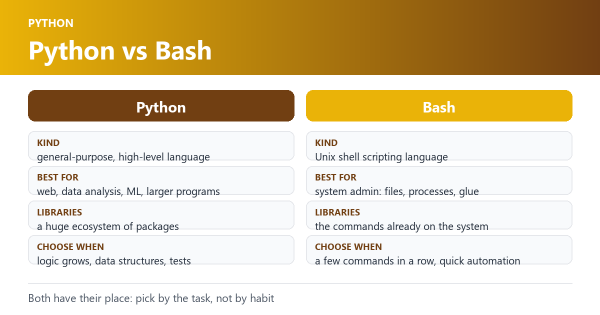
Python and bash are both programming languages, but they have different purposes and use cases.
Ansible is an open-source software platform for automating and configuring computer systems.
Python is a high-level programming language that is widely used for web development, machine learning, scientific computing and more.
In Python, there are no explicit pointers like in some other programming languages. In python everything is an object and references to objects are stored in variables.
In Python, you can define a function with a variable number of arguments using the and syntax in the function definition.
n Python, unlike some other programming languages, there is no explicit syntax for defining interfaces.
Inheritance is a mechanism in object-oriented programming (OOP) that allows you to create new classes that are derived from existing classes.
Let’s learn about decorators @iamdecorator
Learning to write Python code? A Python class is a blueprint for creating objects.
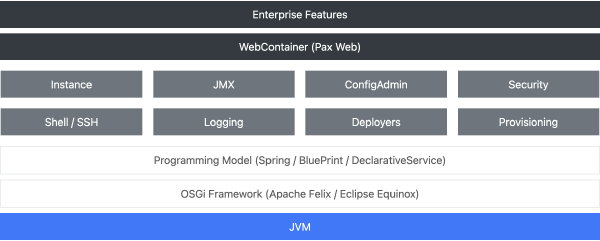
Apache Karaf - I had only heard of it and never had practical exposure to this technology. Main questions in my mind were - What purpose does it serves? and Who uses it?
awk is an interpreted language.
The basic function of awk is to search files for lines that contains certain patterns. When the input line matches the pattern(s), awk performs specified actions on that line.
PKI is the core of security for most organizations, and at its heart is a couple of keys that together allows the encryption/decryption of the traffic exchanged.
A decent developer trick is to ensure your maven points to the right JAVA version, and if you have freshly installed maven it will be pointing to the default available.
I was struggling with the mTLS configuration for zookeeper configuration and somehow no matter what I do I kept getting an error as below
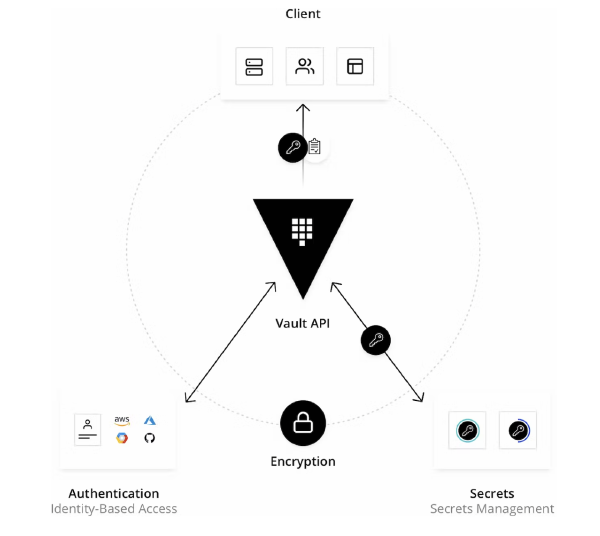
“HashiCorp Vault is an identity-based secrets and encryption management system.”
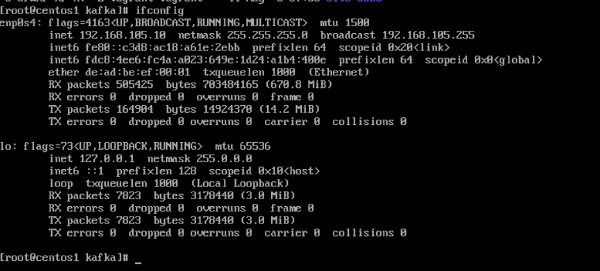
Continuing from where I left in the blog before. If you are using looking to configure a static IP for your machines (may be your use case is similar to mine) this blog might be useful for you.
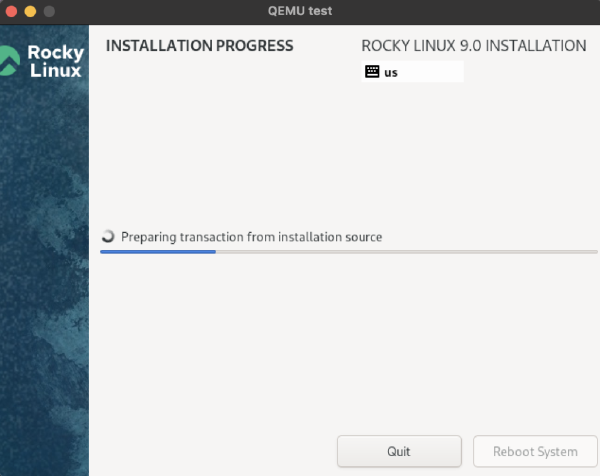
In this blog let’s try and look at some of the commands I used to build an RockyLinux machine on a MacPro M1.
In the previous blog, I was left with the error that had little information for me to debug. I realized since I migrated most of the files from my previous laptop it might be causing an issue.
Having just bought an M1 – MacBook Pro the issue are mounting. The premier challenge was to get my Vagrant boxes configured with provider virtualbox to run.
Open source build automation tool FLEXIBLE and builds any type of software Run on JVM and must have a JDK installed to use it. Gradle models its buils as DAGs pf tasks. Build is graph of tasks Tasks consists of Actions Inputs Outputs Lifecycle Tasks Clean Check Assemble Build Build Configuration Clean Task Gradle evaluates and executes build scripts in three phases Initialization Configuration Execution
Creating a Topic in a kafka-cluster is easy and well documented for the kafka-topics.sh or even the official API documentation.
If you are like me and getting errors while trying to compile your go lang code without having a go.mod in v1.18
Life is bringing it own challenges as I have moved to the United States of America. One of the immediate tech challenge has been using the loaner windows box and still be productive.
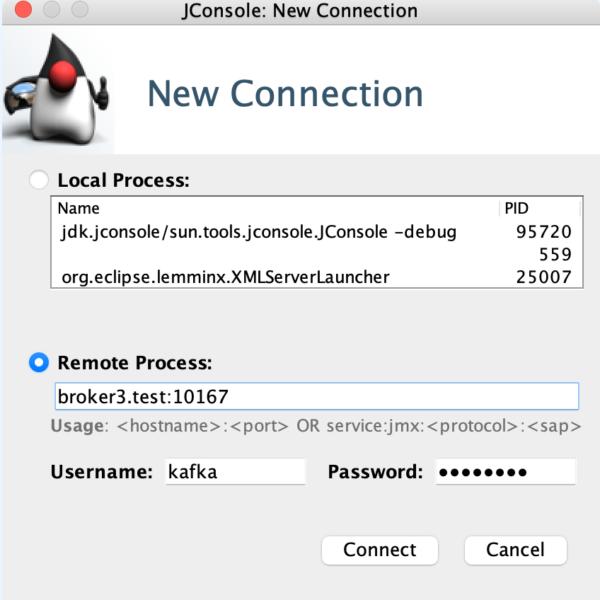
To enable and configure monitoring of Java VM for any java-application using the ready-to-use JMX agent, you must set certain system properties when you start the Java VM.
I never thought the process could be this simple in the year 2022. Thanks to Mr. Gadkari for taking the initiative that the states (some) have already implemented.
Control node Managed nodes Inventory Modules Tasks Playbooks
Bash is different world. Powerful, simple, elegant and complex all at the same time.
– The SSH protocol uses public key cryptography for authenticating hosts and users.
💬 What is SSH protocol?
💬 It is also referred to as Secure Shell, is a method for secure remote login from one computer to another. It is an alternative to telnet and rlogin
Personal notes on Bash: arithmetic, = versus ==, single versus double brackets, and the bc calculator.
If you have seen errors like these when deploying using a serviceAccount
Looking the official diagram from devspace which shows the benefits in detail
So there are many things I have been simultaneously trying to learn & one of those is to learn how you can configure a pipeline
While I continue to learn more about architecture and design of kafka, a quickstart to deploy & test kafka is a must.
Step 1: Add Chart Repo # In my local system it is already present which was confirmed by the listing
A common use-case for cert-manager is requesting TLS signed certificates to secure your ingress resources.
IaC tools like Terraform allows one to manage infrastructure with configuration files rather than through a graphical user interface.
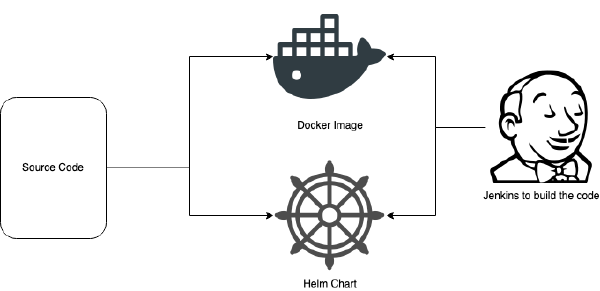
I have written a series of blogs to capture how you can deploy spinnaker on a Kubernetes cluster & manage a helm chart deployment via pipeline.
In this blog let’s try add a helm account and enable for use in the pipelines
You will need a valid docker registry before you add any trigger in the pipeline in Spinnaker
Deploying Jenkins on K8S cluster is as simple as
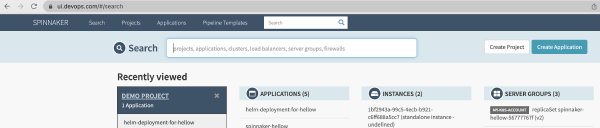
Spinnaker is an open-source continuous delivery platform which provides two core set of features
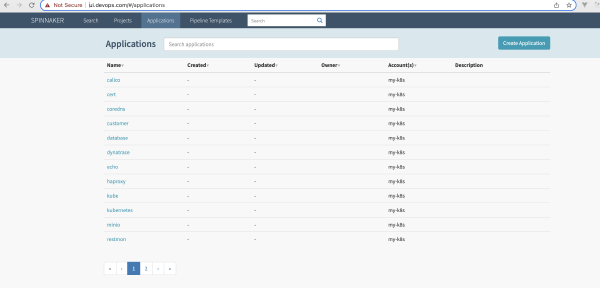
Application Management Application deployment Applications , clusters , and server groups are the key concepts Spinnaker uses to describe your services. Key Concepts # Some of the key concepts in the spinnaker universe are covered as under
While reading Apache Kafka it was interesting analogy that they described
Event streaming is the digital equivalent of the human body’s central nervous system. — Apache Kafka It draws a great parallel between how the central nervous system allows for real time event generations and consumption in terms of reflex actions. The examples are well explained and captured here.

In this blog, I will try add a new node to the already running cluster.
My Cluster # root@master>k get nodes NAME STATUS ROLES AGE VERSION mydevmachine001830.samarthya.me Ready <none> 22h v1.23.1 mydevmachine002687.samarthya.me Ready <none> 41d v1.23.1 mydevmachine003277.samarthya.me Ready <none> 131d v1.23.1 mydevmachine003278.samarthya.me Ready <none> 131d v1.23.1 mydevmachine003417.samarthya.me Ready <none> 4m55s v1.23.1 mydevmachine003968.samarthya.me Ready <none> 131d v1.23.1 mydevmachine003969.samarthya.me Ready control-plane,master 131d v1.23.1 mydevmachine003970.samarthya.me Ready <none> 131d v1.23.1 mydevmachine003979.samarthya.me Ready <none> 29m v1.23.1 Steps to follow # Install docker Install kubeadm, kubectl & kubelet Join the cluster using the token Check the node has joined the cluster Step 1: Install docker # sudo yum install -y yum-utils sudo yum-config-manager \ --add-repo \ https://download.docker.com/linux/centos/docker-ce.repo When adding repo make sure the repo has been added successfully to the machine
India is a complex country, the diversity is ever present and ever growing. What got me going in my deep meditative thinking is having a discussion with my Dad. We have evolved from the just enough generation to over the edge generation. Things that were uncommon during my growing up years and now the basic necessity of this generation.
In this blog I will talk about how you can upgrade a node and the kubernetes cluster version to a specific version.
I have a 6 node local Kubernetes cluster like below
Documentation is a huge part of writing any software. In java you have JavaDoc, which most of the developers adhere to. It is healthy and rich way of exposing the source documentation.
So to delete there was one hard hack way of cleaning it all
What? # Role Based Access Control(s) is a way of regulating access to entities like storage, network etc. RBAC authorization uses rbac.authorization.k8s.io API group. API Objects # There are 4 kind of kubernetes object
Having used SCM plugins for quite sometime, I thought - WHY I have never used them to clone a repository and while I employ the personal access token (NOW)- The weapon of choice, I have never tried it myself.
The only advice I can give to folks who are building helm charts from scratch, is always keep it incremental and do not try to do everything at one go. At least build a decent few before you even try to attempt such a thing, else you will only end up WASTING your precious time on trivial issues which could have been avoided by incremental build, rather than the big bang approach.
In this blog I will walk you through basic steps needed to deploy a Zabbix 5 Agent on a Centos Machine. The Zabbix Release is available here.
Machine # root@node4>cat /etc/redhat-release CentOS Linux release 7.9.2009 (Core) Download and install the RPM
In my cluster things went haywire all of a sudden without a proper showcase, I tried multiple things but it was just not working. Specifically my core-dns and calico-kube-controllers were not coming up and were constantly showing not ready and CrashLoop respectively
In case you are still using the basic/auth it is time to move to personal access token.
Official documentation is the best guide. Personal access tokens (PATs) are an alternative to using passwords for authentication to GitHub Enterprise Server when using the GitHub API or the command line.
Everything starts form a single source file and as the time goes by, it gradually transforms into multiple modules, bulky source files and a source control repository. Mostly by this time the team has already adopted a a build tool, and a repository to publish the versioned artifacts. Journey is similar for every project successful or not.
The concept of profiles let’s a developer define what he wants to build and what to do in specific cases. In this blog I will talk about the problem that I solved using profiles.
All right, it has been sometime since I last wrote my blog, and it has been disappointing not to have found enough time to collate and put my thoughts in a simple worded doc; better late then never. So, here I am trying to reignite the pursuit of writing at least once a week.
योगस्थः कुरु कर्माणि सङ्गं त्यक्त्वा धनञ्जय ।
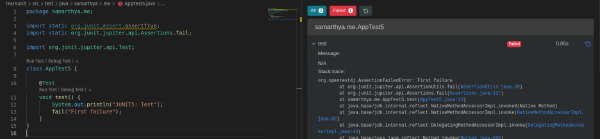
JUnit was developed by Kent Beck and Erich Gamma. Its first version was released in 1997.
JUnit 5 = JUnit Platform + JUnit Jupiter + JUnit Vintage — https://junit.org/junit5/docs/current/user-guide/ It is powerful testing framework, with many modules. These modules are part of three sub-projects
I recently gave CISM and I believe it is easily crackable. For those who are pursuing this certification the mantra is similar (or at least the one that I followed)
Rules that run the organisation = Governance.
Streams are convenient way to reduce the line of codes, but an understanding them is equally challenging. I write this blog, after realising a desperate attempt at solving a trivial problem just took overwhelming time. (Could be that I am getting old, but never late to learn things again)
Code available here.
The ask was to identify the smallest possible integer (> 0) in the array of integers.
Example # 1. [-1,2] -> 1 2. [-1,-2] -> 1 3. [1,3] -> 2 I was initially thinking of using sets and then finding out the missing one, but then reaized it is simpler and I do not need sets
I need to write an app for a friend and what better way to brush up old concepts and write a fresh blog in doing so. So here I am, trying to put together some old and new skills together to help create a simple webapp that will have a dashboard and basic login enabled.
To manage sensitive information you create secrets
k create secret --help Create a secret using specified subcommand. Available Commands: docker-registry Create a secret for use with a Docker registry generic Create a secret from a local file, directory or literal value tls Create a TLS secret Usage: kubectl create secret [flags] [options] Use "kubectl <command> --help" for more information about a given command. Use "kubectl options" for a list of global command-line options (applies to all commands). type specifies the type of secret you are creating (options are as shown above). As I need to create only key value pairs for my dummy secret file I need to know a way of how to facilitate that, and the option -h helped me there
“There are a thousands excuses for failure but never a good reason..”
— Mark Twain
“Losers make excuses, winners make progress.”
— Introduction: The Miracle of self discipline.
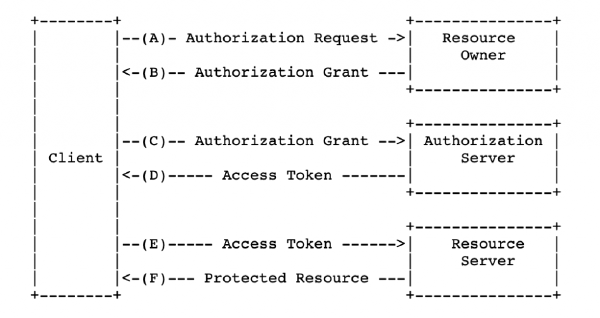
What is OAuth? # From the official definition
It is protocol for Authorization It allows authorization flows for web applications, desktop applications, mobile apps etc.
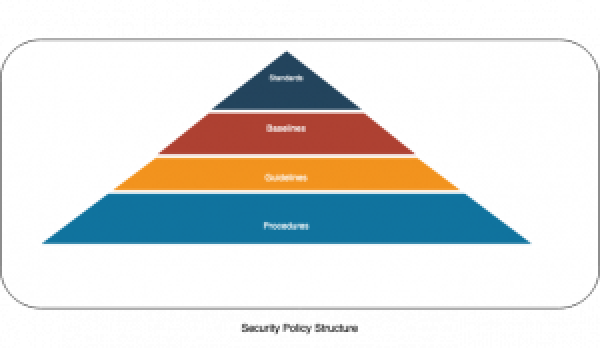
# Standards # Standards are tactical documents that define steps or methods to accomplish the goals and overall direction defined by the security policies.
I just finished my upgrade to Safe Certification and now will be going for CISSP certification. Wish my luck guys!
Some quotes # Effective security plans anticipates change, focuses on specific and achievable objectives, potential problems, and serves as the basis of decision making. Operational plans are the shortest and most frequently updated Tactical plans are mid term plans and supports strategical plans. Strategic plans are the long term plans (usually 5 years) and usually includes risk assessment. Data classification is the primary means by which data is protected based on its need for secrecy, sensitivity and confidentiality. Data classification is the process of organizing objects, subjects, items into groups of similarities (value, cost, vulnerability, risk, power, privilege) Stratify the process of organizing and securing data based on assigned labels of importance and sensitivity. Data classification also addresses how data is removed and destroyed. Security policy is used to assign responsibilities, define acceptable risks, define roles, specify audit requirements and indicate compliance. Security policy are not optional rather mandatory. Three types of security policies are regulatory, advisory and informative.
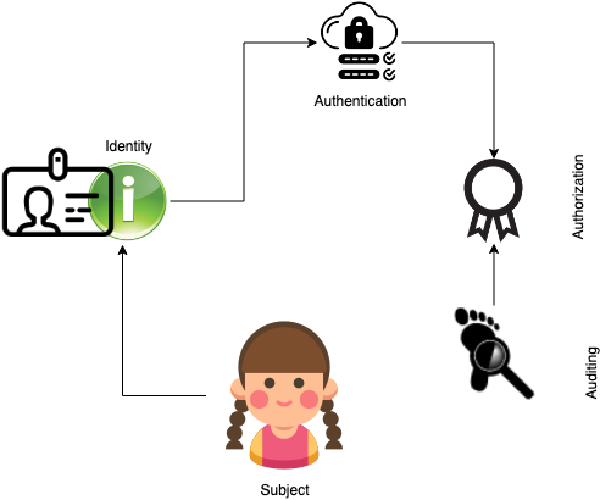
What is an identity? # Identity is the link that correlates the subject and the authentication process. Without a valid identity the system has no way of establishing who the subject is? Identity enables the subject to be identified and validated, and only once it has been established and authorized it is accountable for any actions taken in the system.
GoLang doesn’t have a try and catch like the popular C++ or Java languages, what it has is panic-recover.
I am using Virtual Box 6.1 and will use it to expand the disk space for one my VBox Ubuntu image which was almost full.
Click on File > Virtual Media Manager
Previously I talked about files, encoding in golang. In this LTD (learn to do) I will talk about hash package in general.
https://blog.samarthya.me/wps/2021/01/30/golang-encoding/
Help # https://golang.org/pkg/hash/#Hash https://golang.org/pkg/crypto/#Hash.New https://golang.org/src/crypto/crypto.go?s=364:378#L6 https://golang.org/pkg/crypto/#pkg-subdirectories Package crypto collects common cryptographic constants. — Official golang documentation const ( MD4 Hash = 1 + iota // import golang.org/x/crypto/md4 MD5 // import crypto/md5 SHA1 // import crypto/sha1 SHA224 // import crypto/sha256 SHA256 // import crypto/sha256 SHA384 // import crypto/sha512 SHA512 // import crypto/sha512 MD5SHA1 // no implementation; MD5+SHA1 used for TLS RSA RIPEMD160 // import golang.org/x/crypto/ripemd160 SHA3_224 // import golang.org/x/crypto/sha3 SHA3_256 // import golang.org/x/crypto/sha3 SHA3_384 // import golang.org/x/crypto/sha3 SHA3_512 // import golang.org/x/crypto/sha3 SHA512_224 // import crypto/sha512 SHA512_256 // import crypto/sha512 BLAKE2s_256 // import golang.org/x/crypto/blake2s BLAKE2b_256 // import golang.org/x/crypto/blake2b BLAKE2b_384 // import golang.org/x/crypto/blake2b BLAKE2b_512 // import golang.org/x/crypto/blake2b ) Let’s try out a simple MD5 hasher.
Package encoding provide capabilities to convert data to and from byte-level and textual representations.
In last few blogs I have written about reading commandline parameters reading files and using the os package.
In this blog, I will combine some these items to read a file byte by byte using the bufio package func’s.
In the last blog I talked about command line arguments os.Args[]. In this I will try and create a sample banner program that shall
Take 3 arguments n - Number of times a message has to be repeated. m - The message that needs to be shown. d - If debug message needs to be shown. I am going to use the flags package.
Reading the golang official documentation is fun, today I saw the Variables in package os
var Args []string It allows you to hold command line arguments and a simple main program that can help you validate this.
In the last blog, I tried reading a file in GoLang.
My repository in GitHub has all the code that I write (link) Now, I will extend the same program to write to the same file.